The revelation of an attack on the software supply chain unleashed a wave of reactions in the cryptocurrency community. Researchers discovered malicious updates in NPM packages, a key tool for development in JavaScript, which generated concern about the impact it could have on the security of millions of Wallets. The account of a renowned developer, identified as «Qix», was compromised, which allowed the publication of altered versions of broad -use bookstores. They were inserted a malware capable of detecting the presence of wallets such as MetamSk and manipulating transactions in real time. As cryptootics reported, The malicious code intercepts the data before they arrive at the Wallet, modifies the address of the recipient and forward the operation to the userwho, without noticing, ends up signing shipments to directions controlled by the attackers. Although the attack is mainly oriented to developers, the magnitude of the distribution of these packages makes it an indirect threat to millions of end users, especially for those who store cryptocurrencies in Wallets connected to the Internet. The news generated a strong impact on the community. Changpeng Zhao (CZ), former CEO of Binance, warned: «Even open source software is no longer safe. Web3 will redefine security for web2. We are still at an early stage ». With this comment, CZ stressed that confidence in open source software does not guarantee immunity against vulnerabilities In the supply chain. Although these types of programs can be audited by the community, the magnitude of the ecosystem and the dependence on external libraries open doors to difficult attacks.
Other actors described the attack as one of the most severe in recent history. Quinten François, co -founder of Werrate – a community review platform based on trust and authenticity – defined it as «the greatest hacking of the supply chain ever seen», highlighting that NPM is a tool used by millions of applications and Wallets of Bitcoin and cryptocurrencies worldwide. François stressed that even Wallet Hardware users must carefully review each transaction before signing it and, following the recommendation of the Ledger CTO, advised to temporarily suspend the on-chain transfers if this type of devices is not available.
Latin American specialists warn about the impact
From Latin America also arose warnings about the attack. Specialists from the region emphasized the importance of properly protecting funds and extreme precautions. The analyst known as Btcandres was blunt: «You must meticulously verify each character of the recipient’s address in its wallet application or on the screen of his hardware wallet before approving any transaction.» He also said that the malicious script contains extensive addresses belonging to the attackers, covering multiple cryptocurrencies, including Bitcoin (BTC), Ethher (Eth), Solana (Sol), Litecoin (LTC) and Bitcoin Cash (BCH). For his part, Manuel Ferrari, president of the Argentine Bitcoin NGO Always verify the complete address that appears on the device screen before signing a transactionnot limited to checking only the first or last characters. He recalled that, if an error is made and the funds are sent to an incorrect address, there is no way to recover them: «In Bitcoin there is no back.»
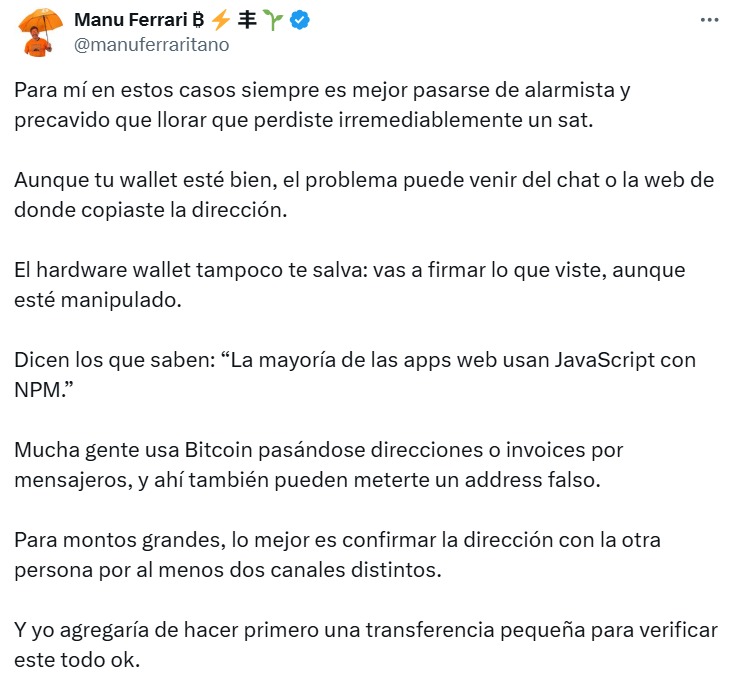
Making a small transfer first to verify that everything is in order can avoid more than a disgust. Source: @manuferraritano. Ferrari also suggested to migrate to software that does not depend on NPM, such as Sparrow Wallet, and use it together with compatible Wallet Hardware, including Trezor, Ledger, Bitbox, Jade or Keystone. In the case of devices without screen, such as Bitkey or Tangm, he urged to temporarily suspend operations until safe updates are published. In the midst of the alerts for the attack, it is important to mention that the educational community Cuba Bitcoin reported that it received a 10 -hardware buckstream jade lot, donated by the educational academy my first bitcoin of El Salvador and by Blockstream. These devices will be used to provide self -ocustody workshops throughout the country, and according to the Blockstream equipment their product «does not use JavaScript or NPM, so neither the application nor the Jade devices have been affected by the current attack on the NPM supply chain». However, from the company they also asked to carefully verify the addresses when sending and receiving funds. After the propagation of the NPM supply chain attack, the main Wallet companies in Bitcoin and cryptocurrencies issued communications ensuring that their tools were not compromised. Ledger and Trezor confirmed that their custody devices do not include vulnerable technologies. Other popular Wallets, such as Sparrow, Blockstream Jade, Wasabi, Electrum, Coldcard, Seedsigner, among many others, also reported that they remain unharmed. On the other hand, the Rani Haddad researcher, using the Arkham Intelligence monitoring platform, identified some wallets linked to the attacker, which show a total balance of just 500 dollars distributed in several cryptocurrencies, indicating that the real economic impact was minimal. The truth is that, although not all end users are directly affected, the episode makes it clear that The safety of funds depends largely on manual verification and the use of specialized devices. Prevention and detail attention are, in these cases, the best defense against attacks that seek to exploit ecosystem infrastructure. In the case at hand, it is best to temporarily suspend the on-chain operations. However, the manual verification of each character of the recipient’s address remains a valid advice at all times.